How traffic reaches your application
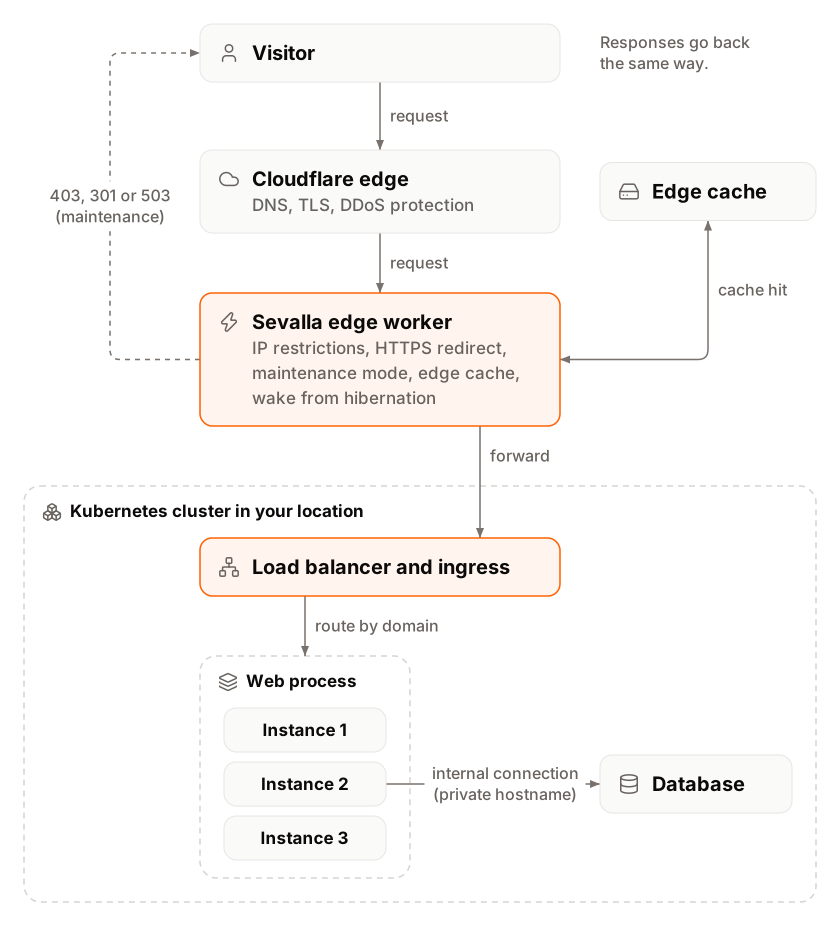
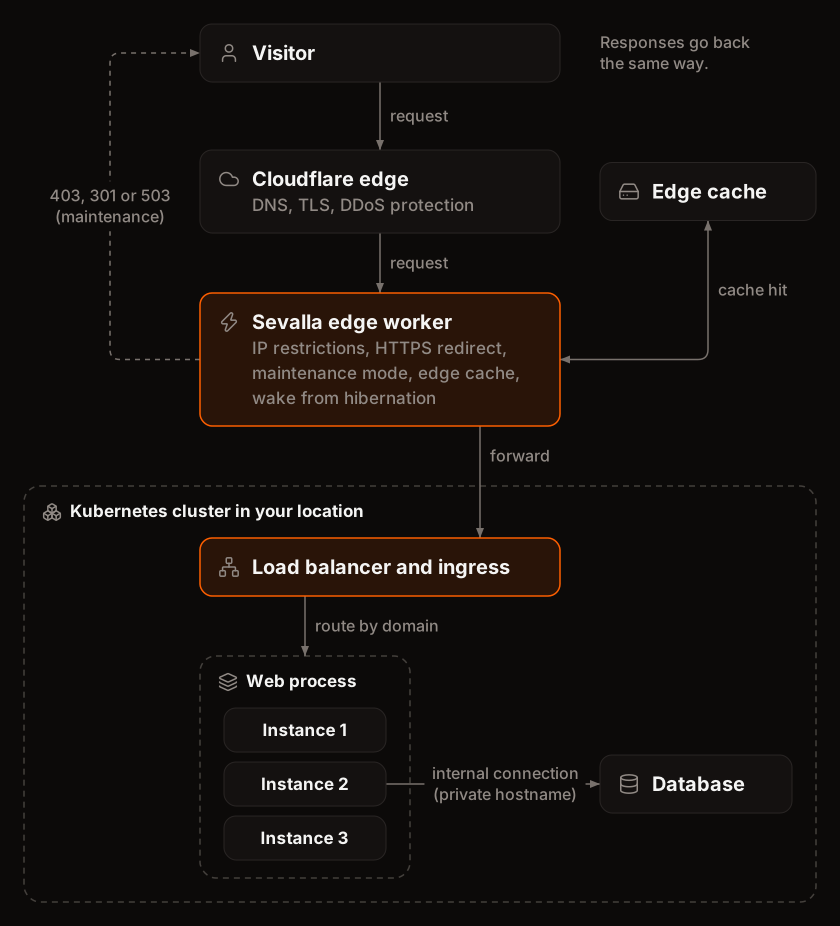
- A visitor opens one of the application’s domains on port 443. Cloudflare answers, redirects plain HTTP (port 80) to HTTPS with a
301, and applies IP restrictions, maintenance mode and caching. - Cloudflare forwards the request to the application’s location, where Sevalla routes it to an instance of the web process on the web process port,
8080by default. The request carries the headers Cloudflare and Sevalla add. - Non-HTTP clients connect through a TCP proxy instead, and your other services use internal hostnames on the private network.
sevalla.app domain. See Instance sizes.
Web process port
The web process port is the port your web server listens on inside its container. Every domain of the application routes to it. It’s8080 by default, and Sevalla sets the PORT environment variable to it, so the safest setup is a server that listens on PORT:
server.js
0.0.0.0 (all interfaces), not localhost or 127.0.0.1, or requests can’t reach the server.
1
Open the Networking tab
In the sidebar, click Applications, then click the application. Click the Networking tab.
2
Update the port
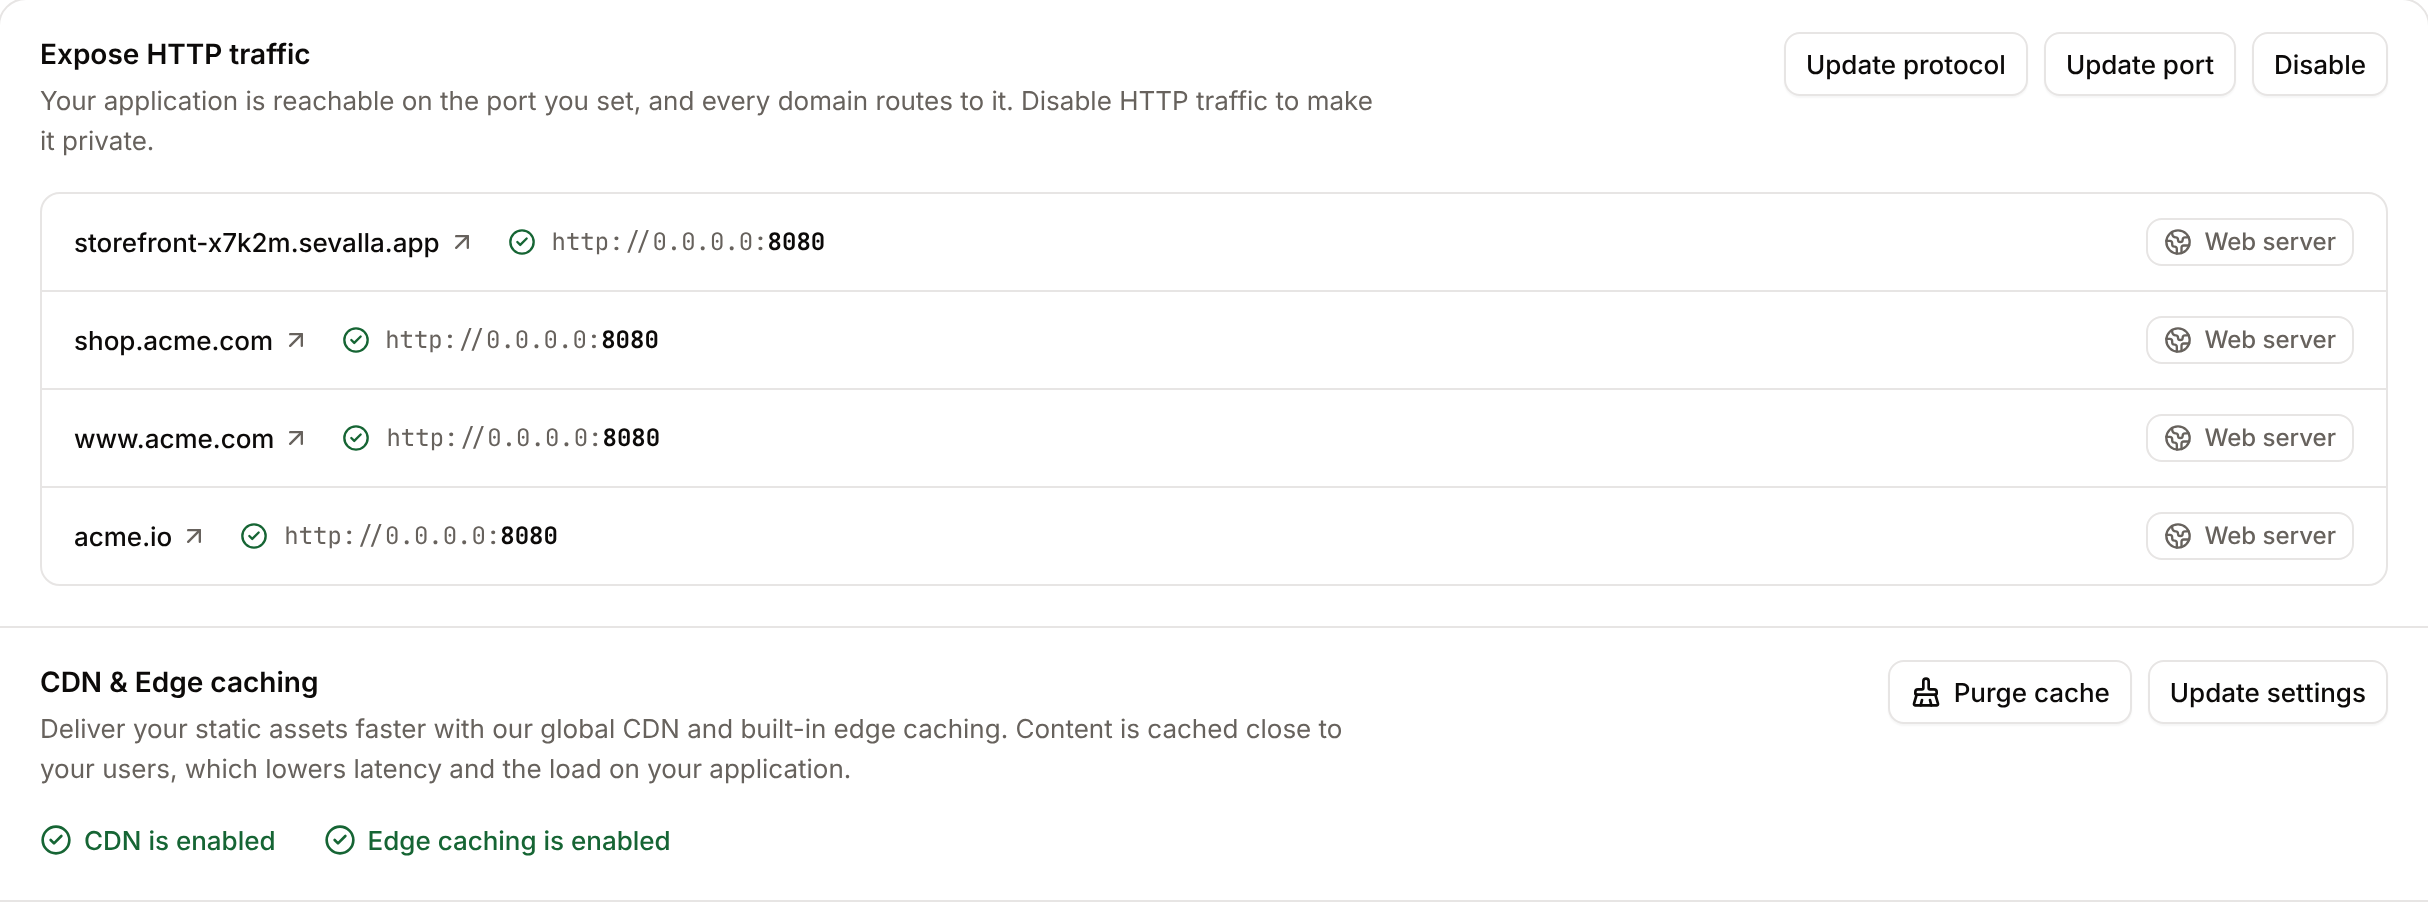
In Expose HTTP traffic, click Update port, enter the Port your web process listens on, and click Update port.
8080 instead, so pick another port. Sevalla applies the change to the running web process without a new deployment, and the domains in the section show the new port, for example http://0.0.0.0:3000.
Use gRPC
The web process speaks HTTP by default. To serve gRPC, click Update protocol in Expose HTTP traffic, pick gRPC in Protocol, and click Update protocol. Your web process must then serve cleartext HTTP/2 (h2c) on its port; Cloudflare and Sevalla handle TLS. The section’s title changes to Expose gRPC traffic. Switch back the same way.Turn HTTP traffic off
Turn HTTP traffic off to make an application private: its web process stops receiving requests and its domains stop answering, while every process keeps running. Use it for an API that only your other services call over an internal connection.1
Disable HTTP traffic
In Expose HTTP traffic, click Disable.
2
Confirm
In the Disable HTTP traffic dialog, click Disable HTTP.
IP restrictions
IP restrictions allow or block HTTP traffic by the visitor’s IP address. Cloudflare checks every request to every domain of the application before anything else, and a blocked request gets a403 with the body Forbidden.
Each entry is an IPv4 or IPv6 address (
203.0.113.7) or a CIDR block (203.0.113.0/24). There’s no limit on the number of entries. Only one mode is active at a time.
1
Open IP restrictions
On the application’s Networking tab, click Update IP restrictions.
2
Pick a mode and the addresses
Choose IP allowlist or IP denylist. Enter an address or CIDR block, and click Add IP address for each one more.
3
Save
Click Update IP restrictions.
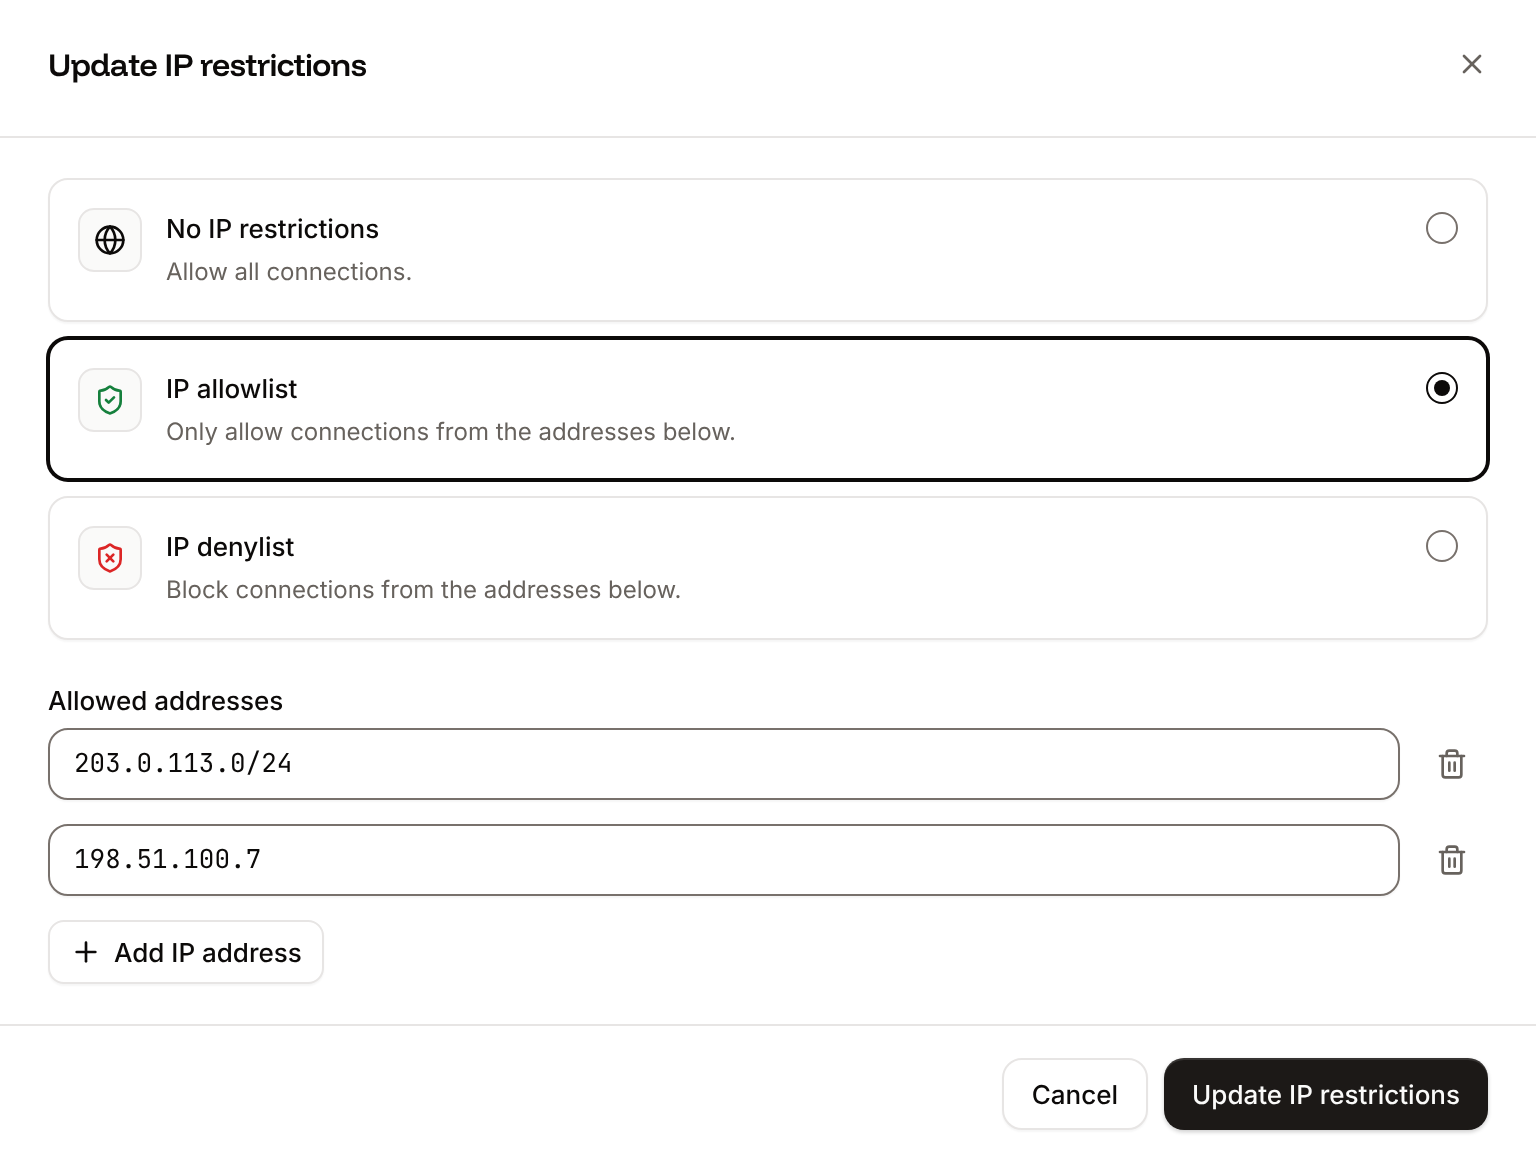
Invalid IP address or CIDR, and repeated ones This address is already in the list.
IP restrictions apply to HTTP traffic on the application’s domains. They don’t apply to TCP proxies or to the private network.
TCP proxies
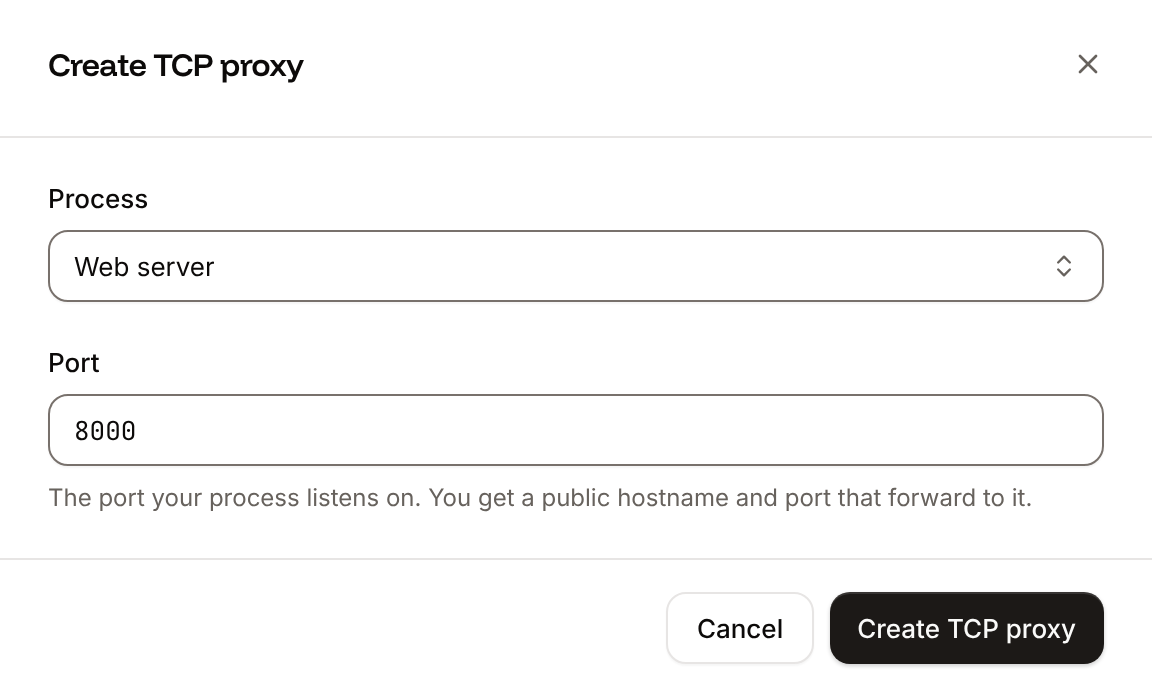
A TCP proxy gives a process a public hostname and port for traffic that isn’t HTTP, such as a database you run yourself, a message broker, or a WebSocket server running as a background worker. Connections to the proxy’s hostname and port are forwarded to the port the process listens on.1
Open the form
On the application’s Networking tab, click Create TCP proxy.
2
Pick the process and port
Pick the Process, enter the Port it listens on (default
8000), and click Create TCP proxy.storefront-x7k2m-a1b2c.ext.sevalla.app:24817) next to the process port. Sevalla applies it to the running process without a new deployment. Connect your clients to that address.
Legacy TCP proxy endpoints
TCP proxies created before the current endpoints used a hostname of the form<cluster>.proxy.sevalla.app and a port from 30000 to 30999. Those legacy hostnames and ports were disabled on Oct 15, 2026, and connections to them fail. If the dashboard shows Your TCP proxy endpoint has changed (or endpoints have changed), update your clients to the address listed for each proxy; Show legacy endpoints lists the old ones for reference. See Legacy TCP proxy and external connection endpoints.
Egress IP addresses
Egress IP addresses are the public addresses that the application’s outbound connections come from, for example to an external database, a payment API or a mail provider. If the service you connect to restricts access by IP, allowlist these addresses there. The Egress IP addresses section of the Networking tab lists them, and what you get depends on the location:Egress addresses are shared with other workloads in the same location, so an allowlist entry doesn’t identify your application alone. Where the external service supports it, also authenticate with credentials such as an API key or a username and password.
Oracle Cloud egress IP addresses
When an application moves to Oracle Cloud Infrastructure, its egress address changes to the one of its new location. Update IP-based allowlists before the move.
Internal hostnames
Every web process and background worker has an internal hostname that your other services use to reach it on the private network, without leaving the data center. It has the form<application name>-<process key>.<application name>.svc.cluster.local; the web process’s key is web, for example storefront-x7k2m-web.storefront-x7k2m.svc.cluster.local. The Internal hostnames section lists each process’s hostname with a copy button.
Another service reaches the hostname only through an internal connection, on the web process port or a private port. Cron jobs and jobs have no internal hostname.
Internal connections
An internal connection opens the private network between this application and a database or another application in the same location. Traffic over it stays inside the data center and doesn’t pass through Cloudflare. Use it instead of a database’s external connection whenever both services run on Sevalla.Both services must be in the same location, and you need permission to update both. To connect services in different locations, clone the application into the database’s location.
1
Open the form
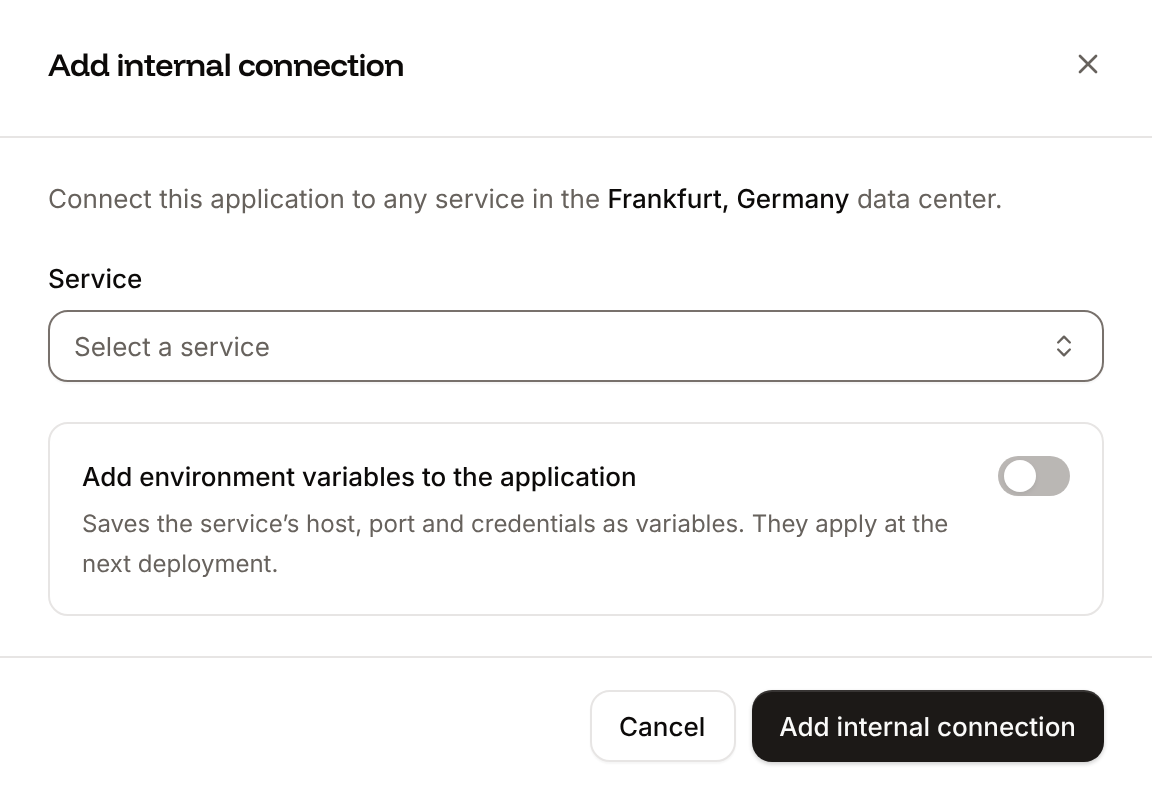
On the application’s Networking tab, in Connected services, click Add internal connection.
2
Pick the service
In Service, pick an application or database. The list shows the services in the same location that aren’t suspended or connected yet.
3
Add the variables
Turn on Add environment variables to the application to save the service’s host, port and credentials as environment variables. Rename the keys if your framework expects other names, and choose Available during runtime and Available during build.
4
Connect and deploy
Click Add internal connection, then deploy the application so it gets the new variables.
Private ports
A private port exposes another port of a web process or background worker on the private network, for example a metrics endpoint or a gRPC port next to the HTTP one. Connected services reach it on the process’s internal hostname.1
Open the form
On the application’s Networking tab, in Private ports, click Expose private port.
2
Pick the process and port
Pick the Process, enter the Port it listens on, and click Expose port.