The Sevalla team redeployed every running and hibernated PHP application that used an affected release, without the build cache and with no change to your code. A hibernated application stays asleep and runs the patched release when it wakes. Suspended applications weren’t redeployed: redeploy one right after you activate it. On the application’s Deployments tab, the Sevalla team’s deployment shows Sevalla team as the person who started it, with the note
Important PHP security patch: CVE-2026-109618 and CVE-2026-109619. The team couldn’t redeploy every application: if the deployment failed or is missing, see If the Sevalla team deployment failed. A redeploy doesn’t upgrade a PHP release your code pins (If redeploying does not upgrade PHP) or PHP 8.1 and older (If you cannot upgrade PHP).Redeploy your application
Redeploy the live deployment without the build cache: the new build installs the patched PHP release, with no change to your code. This works for Nixpacks, Railpack and Buildpacks, and for most Dockerfile builds. Do it for every PHP application.1
Open the latest successful deployment
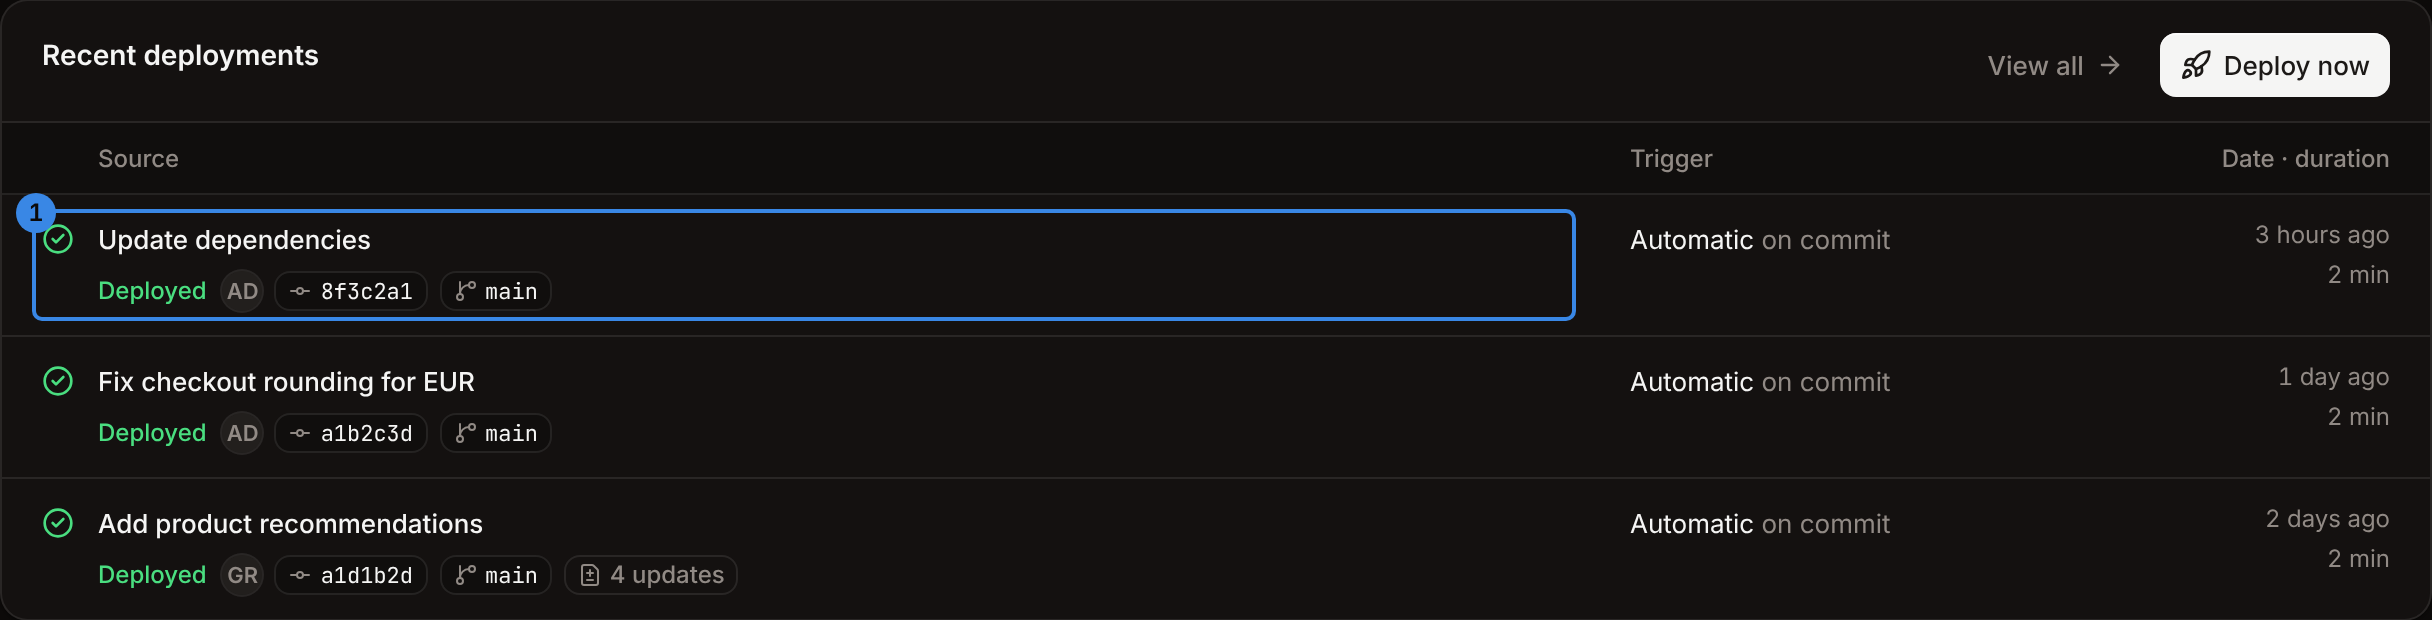
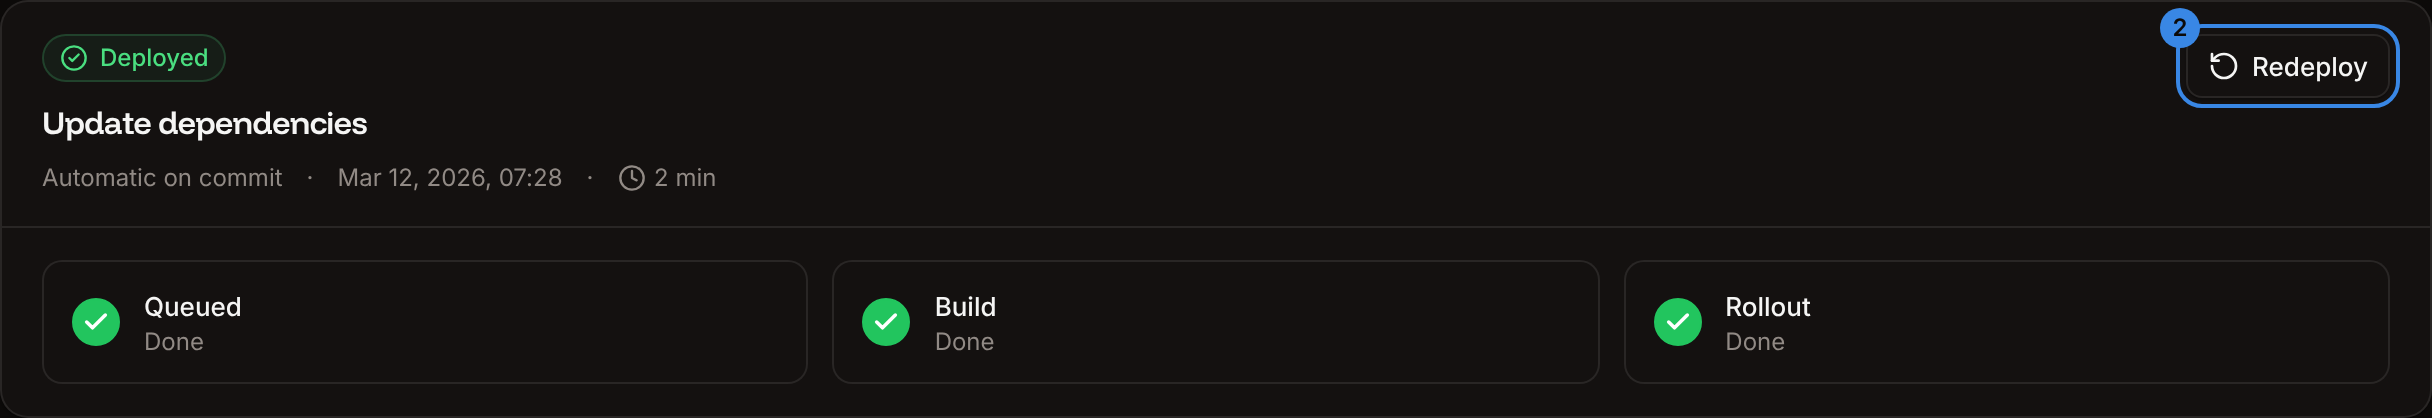
In the sidebar, click Applications, then click the application. On the Overview tab, in Recent deployments, click the most recent deployment with the status Deployed.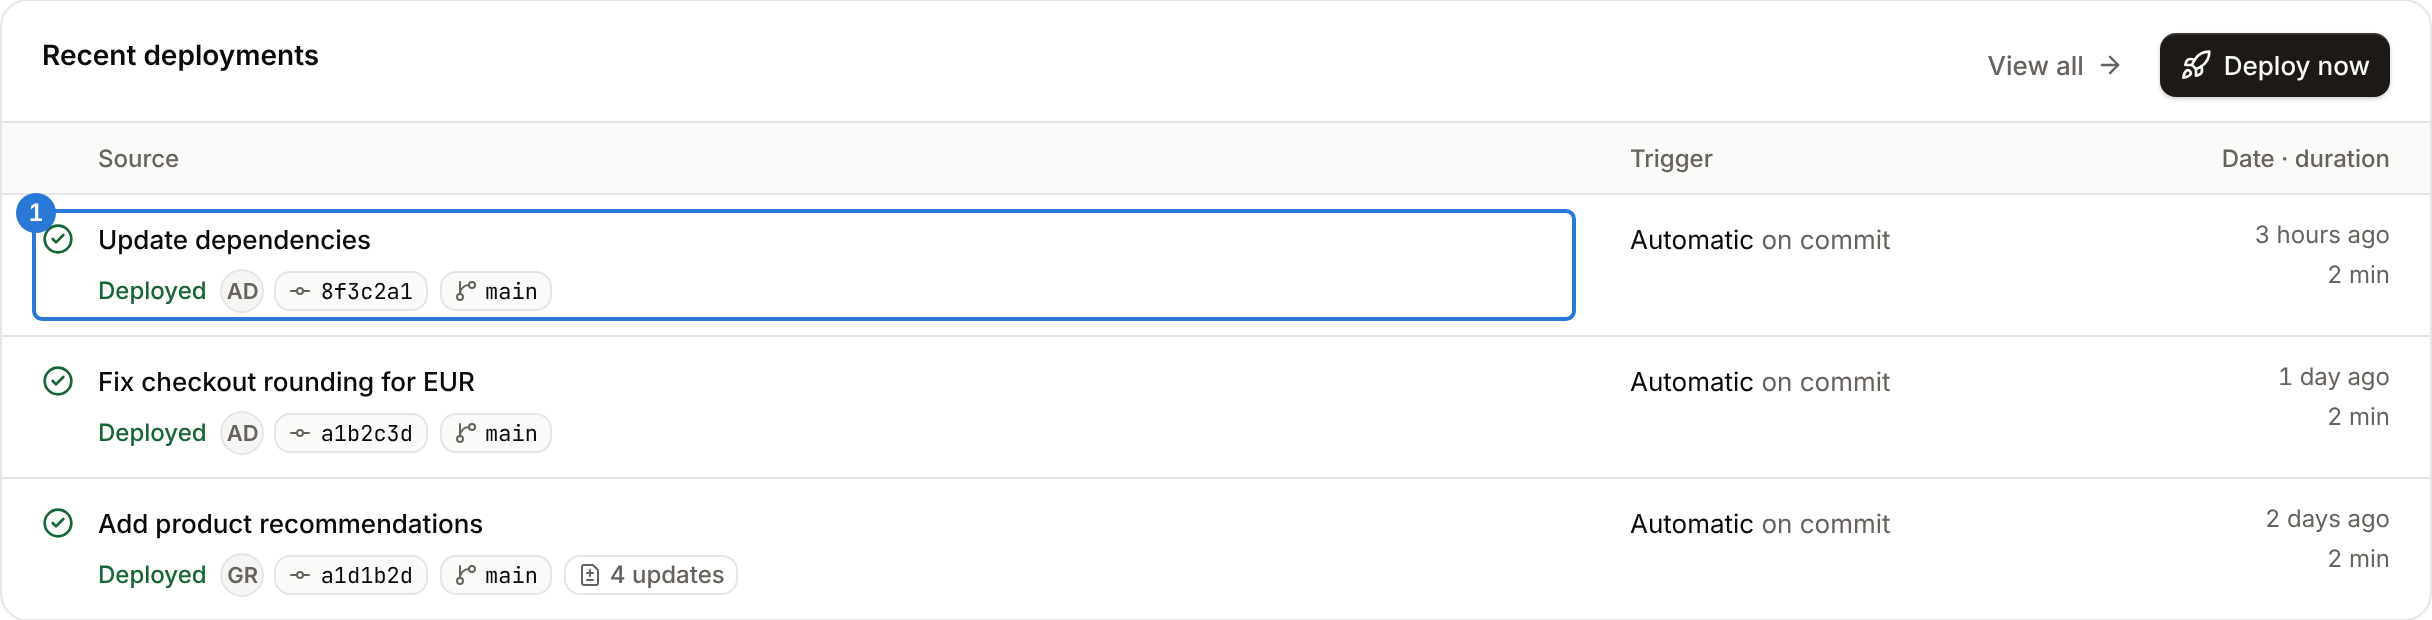
2
Click Redeploy
On the deployment’s page, click Redeploy.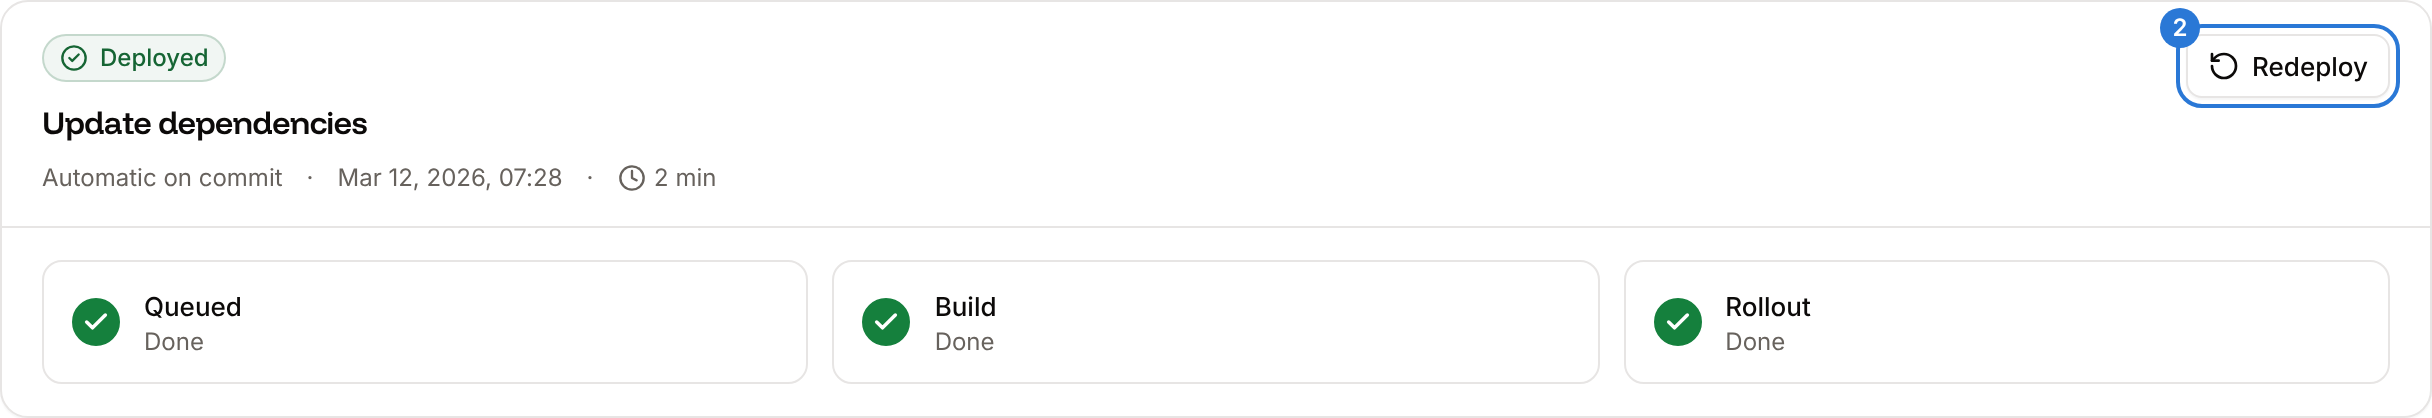
3
Skip the build cache
In the Redeploy dialog, select Skip build cache.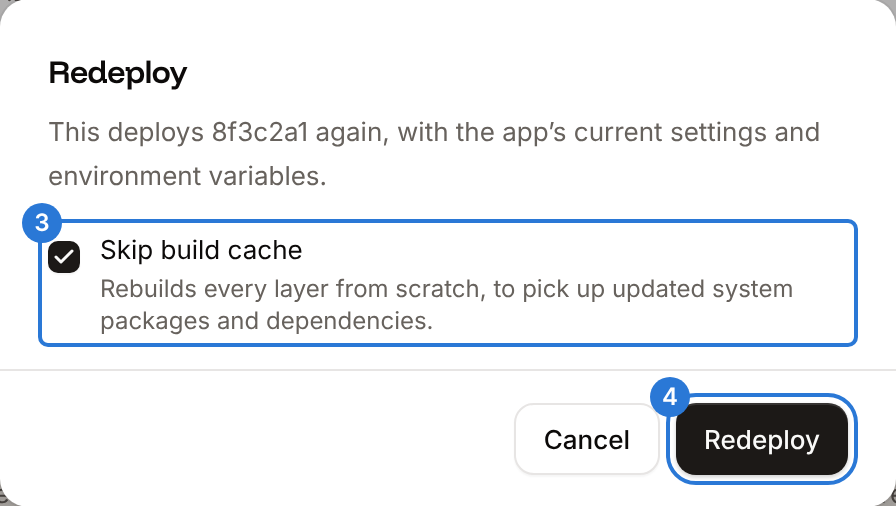
4
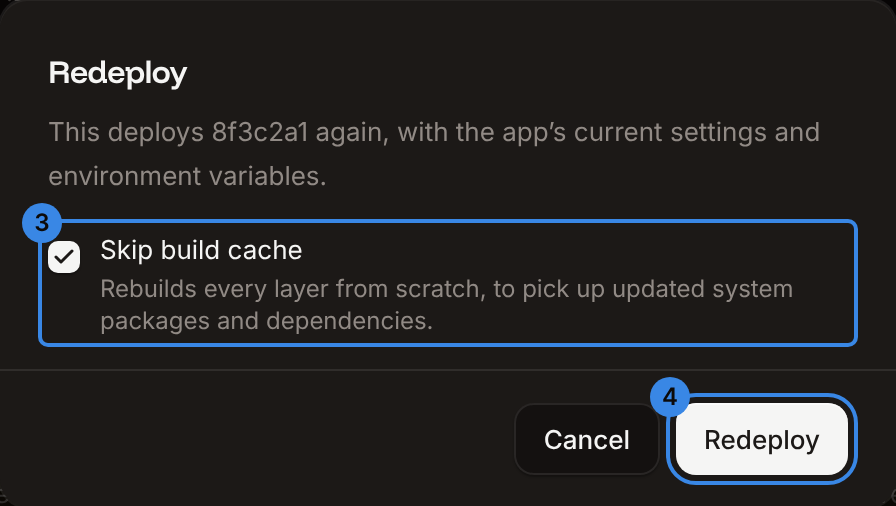
Redeploy
Click Redeploy. A new deployment of the same commit starts.
php -v in the application’s Web terminal tab. It prints the fixed release of your PHP branch:
If it still prints an older release, see If redeploying does not upgrade PHP.
If the Sevalla team deployment failed
When the Sevalla team deployment fails, the application keeps running its previous deployment, so it still runs the affected PHP release. Open the deployment on the application’s Deployments tab, find the error in its log, fix the cause, then redeploy the application. If the application has no Sevalla team deployment, Sevalla couldn’t read its Git repository. Check the repository in the application’s Source settings and give Sevalla access to it again (GitHub, Bitbucket, GitLab), then redeploy it.Check for signs of an attack
A new deployment replaces the files in your instances, but not the files on a disk. If the application ran an affected PHP release, look for.php files on its disks that you didn’t add, such as files in an uploads folder. If you find any, delete them, then change the secrets the application can read: environment variables, database passwords and API keys.
If redeploying does not upgrade PHP
A redeploy keeps the PHP release your code pins. Change the pin, commit it, and deploy the new commit:- Dockerfile: the
FROMline pins a full release, such asFROM php:8.4.26-apache. Change it to the patched release of your branch, such asFROM php:8.4.27-apache. Moving tags, such asphp:8.4-apacheanddunglas/frankenphp:1-php8.4, already point to the patched images. - Railpack and Buildpacks:
require.phpincomposer.jsonpins an exact release, such as"php": "8.4.26". Change it to a range such as"^8.4"and runcomposer update --lock, then commit both files. - Buildpacks on
heroku/builder:20: this builder doesn’t get the patched releases. Switch the pack builder toheroku/builder:22(see Pack builders).
If you cannot upgrade PHP
When you can’t upgrade PHP yet, for example on PHP 8.1 or older, add three PHP settings. They make the attack harder but don’t fully fix it, so upgrade PHP as soon as you can. Adding them takes one deployment and no changes to your code.- Nixpacks
- Railpack
- Buildpacks
- Dockerfile
1
Add the settings file
Add a
php-conf.d folder to the build path, with this php.ini file in it:php-conf.d/php.ini
2
Point PHP at it
Add the environment variable
PHPRC with the value /app/php-conf.d, with Available during runtime and Available during buildtime both selected.3
Deploy
Deploy the application.
php -i | grep -E "upload_progress|memory_limit" prints memory_limit => -1 => -1 and session.upload_progress.enabled => Off => Off.Use PHPRC, not PHP_INI_SCAN_DIR. Nixpacks loads PHP’s extensions through PHP_INI_SCAN_DIR, so setting it removes them and the build fails with The iconv OR mbstring extension is required and both are missing.
Set them only as shown, not with
ini_set() or a .user.ini file, and don’t let your code set memory_limit back to a number. If you pass PHP settings per request (php_value or php_flag in .htaccess, or fastcgi_param PHP_VALUE in an nginx configuration), move them to php.ini. Once PHP is upgraded, you can remove the settings.
Update history
More information
- PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 release announcements
- GHSA-w8hw-w9fx-j79w (CVE-2026-109618)
- GHSA-6wmf-4rv5-p3rp (CVE-2026-109619)