How SAML SSO works
A person clicks Sign in with SSO on the Sevalla sign-in page and enters their work email. Sevalla finds the company whose SSO domain matches the email, sends them to that company’s IdP, and signs them in when the IdP sends back a signed response for the same email address. See Sign in with SSO.- Sign-in starts at Sevalla. Signing in from the IdP’s app dashboard (IdP-initiated sign-in) isn’t supported, because Sevalla only accepts responses to requests it sent. Hide the Sevalla app tile in your IdP so people don’t try it.
- One domain per company, one company per domain. A company has one SSO email domain, and a verified domain can be used by only one company. Only people whose Sevalla email address is on that domain can use SSO for the company.
- The domain is a single name and a top-level domain, such as
example.com. Subdomains and multi-part suffixes such asmail.example.comorexample.co.ukaren’t accepted. - No Sevalla two-factor code. People who sign in through the IdP skip Sevalla’s two-factor authentication; the IdP handles authentication.
- Your IdP sets the session length. An SSO session lasts until the time your IdP puts in its response. If the IdP doesn’t set one, the session lasts 24 hours. When it ends, a company with mandatory SSO asks the person to authenticate through the IdP again.
- Responses must be signed. The IdP must sign the SAML response, the assertion, or both. Sevalla rejects unsigned responses.
- Certificates expire. Starting 21 days before the IdP certificate saved in Sevalla expires, Sevalla emails the company’s owners and admins so they can update it.
Identity provider guides
Step-by-step guides show where each value goes in the most common identity providers. Any other SAML 2.0 identity provider works too, using the values in Set up the app integration in your IdP.Google Workspace
Add a custom SAML app in the Google Admin console.
Microsoft Entra ID
Create an enterprise application with SAML sign-on.
Okta
Create a SAML 2.0 app integration.
OneLogin
Use the SAML Custom Connector (Advanced).
PingOne
Add a SAML application in your PingOne environment.
Before you begin
- You’re a company owner or admin. Only they see Single sign-on in the sidebar.
- You can create applications in your identity provider.
- You can add a TXT record to the DNS of your email domain, unless Sevalla can verify the domain without one.
- Your own Sevalla account uses an email address on that domain, and your IdP lets that account use the new app. The setup test signs you in through the IdP with your own account.
Start the setup
1
Open single sign-on
In the sidebar, under Company, click Single sign-on.
2
Start the wizard
On the Single sign-on card, click Enable. The Configure SSO wizard opens on its Introduction step, which lists the steps ahead. Click Continue.
Set up the app integration in your IdP
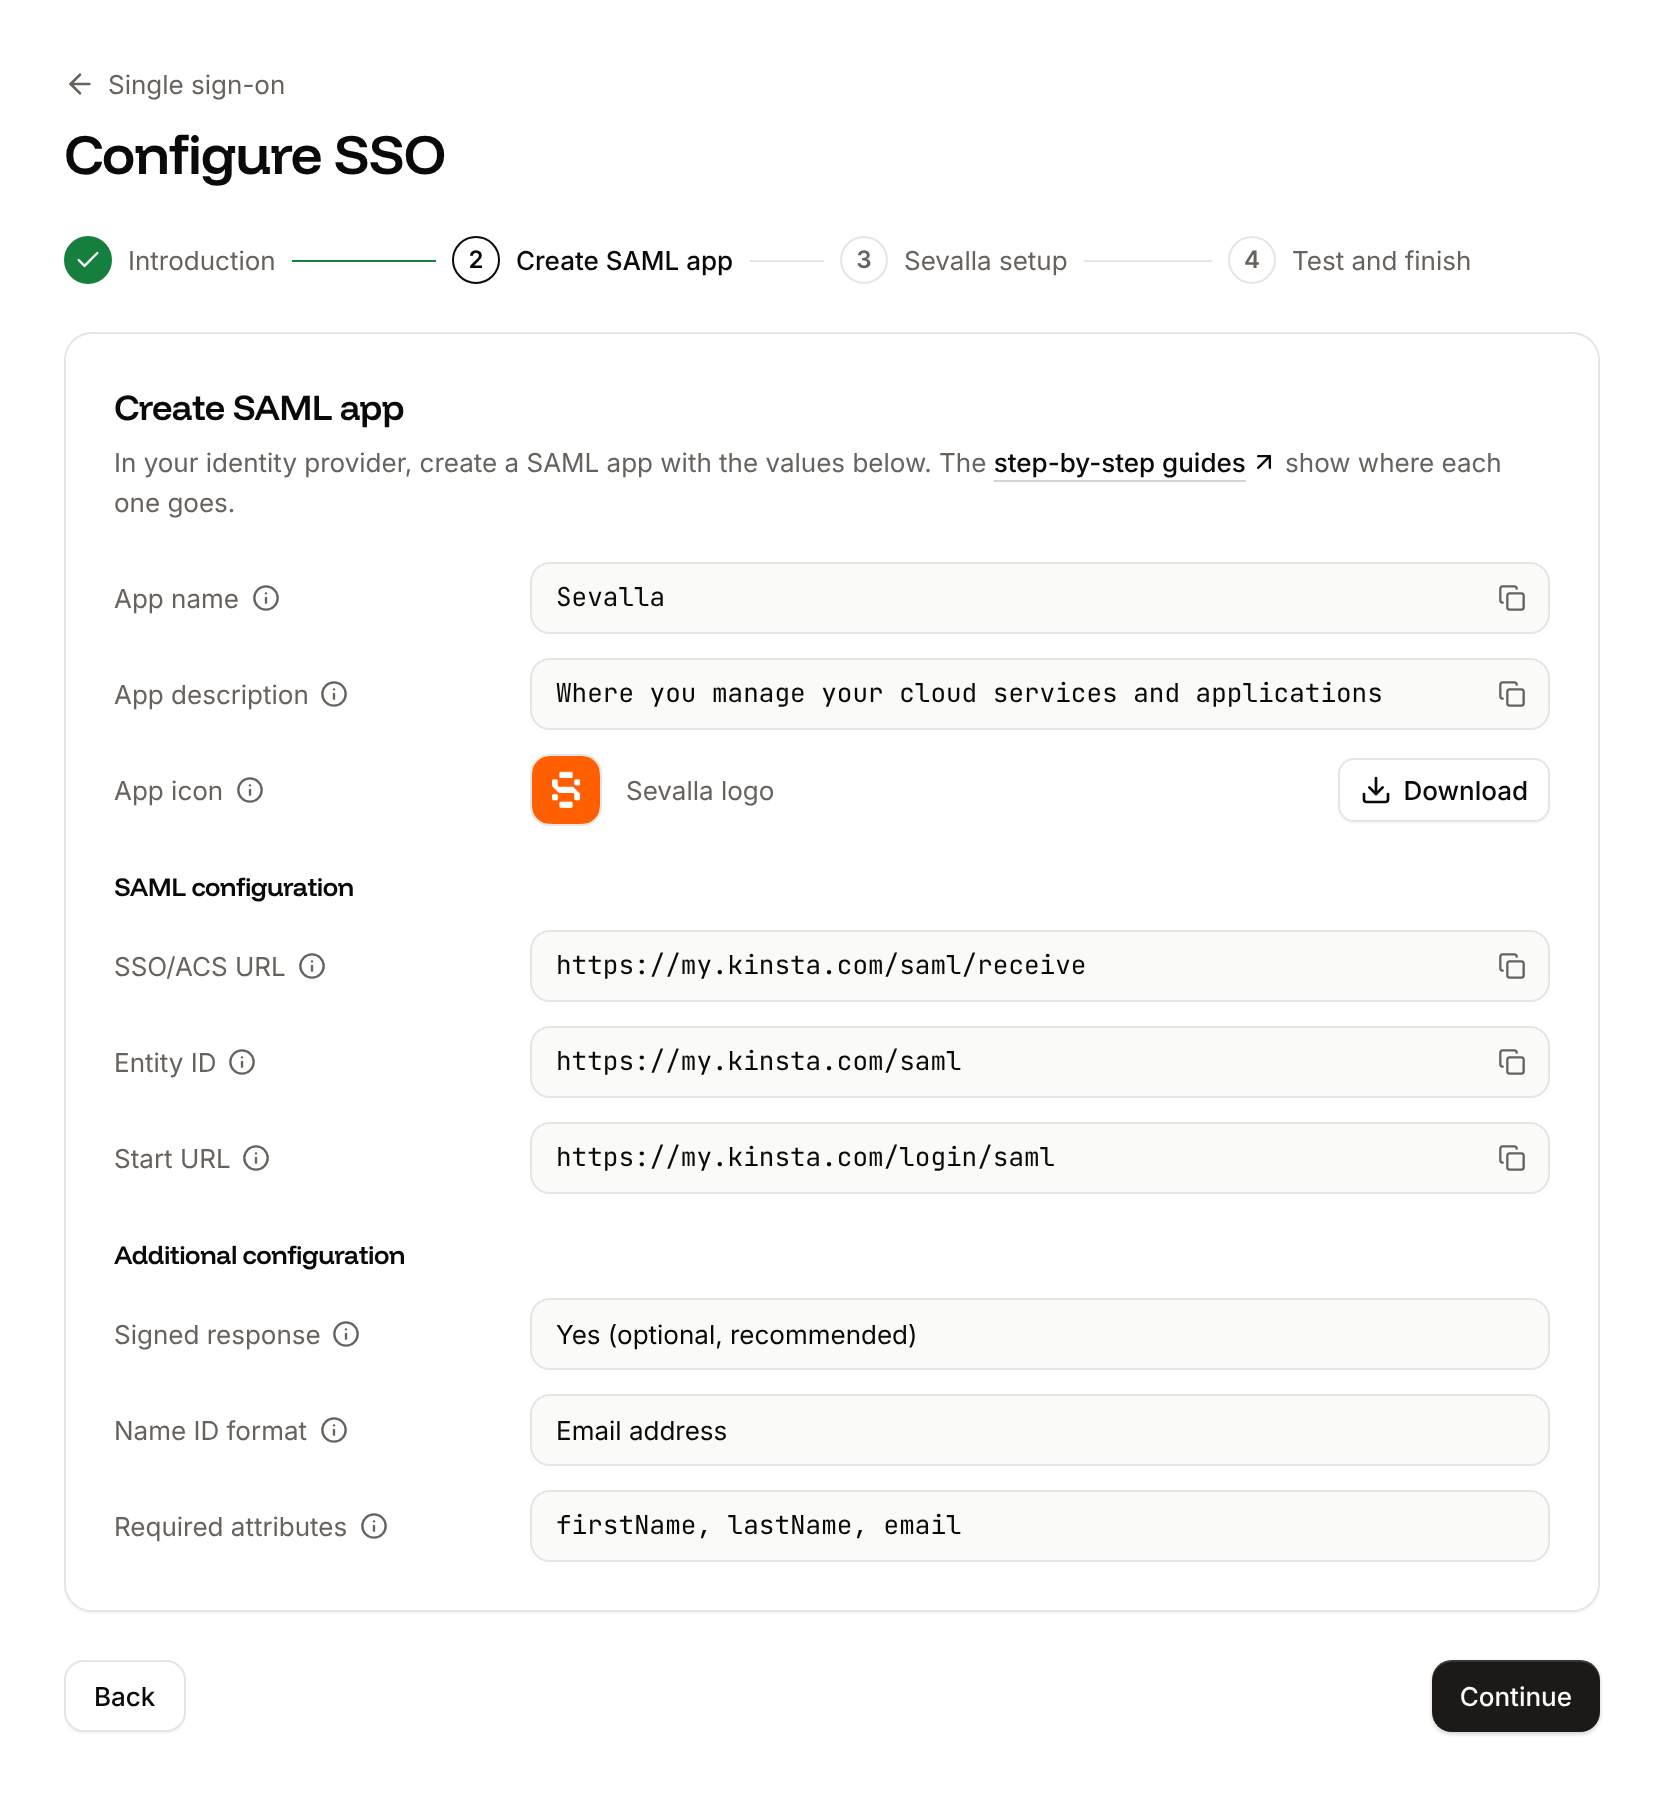
The Create SAML app step shows the values to enter in a new SAML app in your identity provider, each with a copy button. Create the app with these values, then click Continue. The identity provider guides show the exact fields.
Sevalla is a Kinsta product, so these URLs use
my.kinsta.com. That’s expected.
Map the three attributes with exactly these names. email must be the address the person uses in Sevalla (if it’s missing, Sevalla uses the Name ID). Sevalla uses firstName and lastName to name accounts it creates for new people.
Verify your email domain
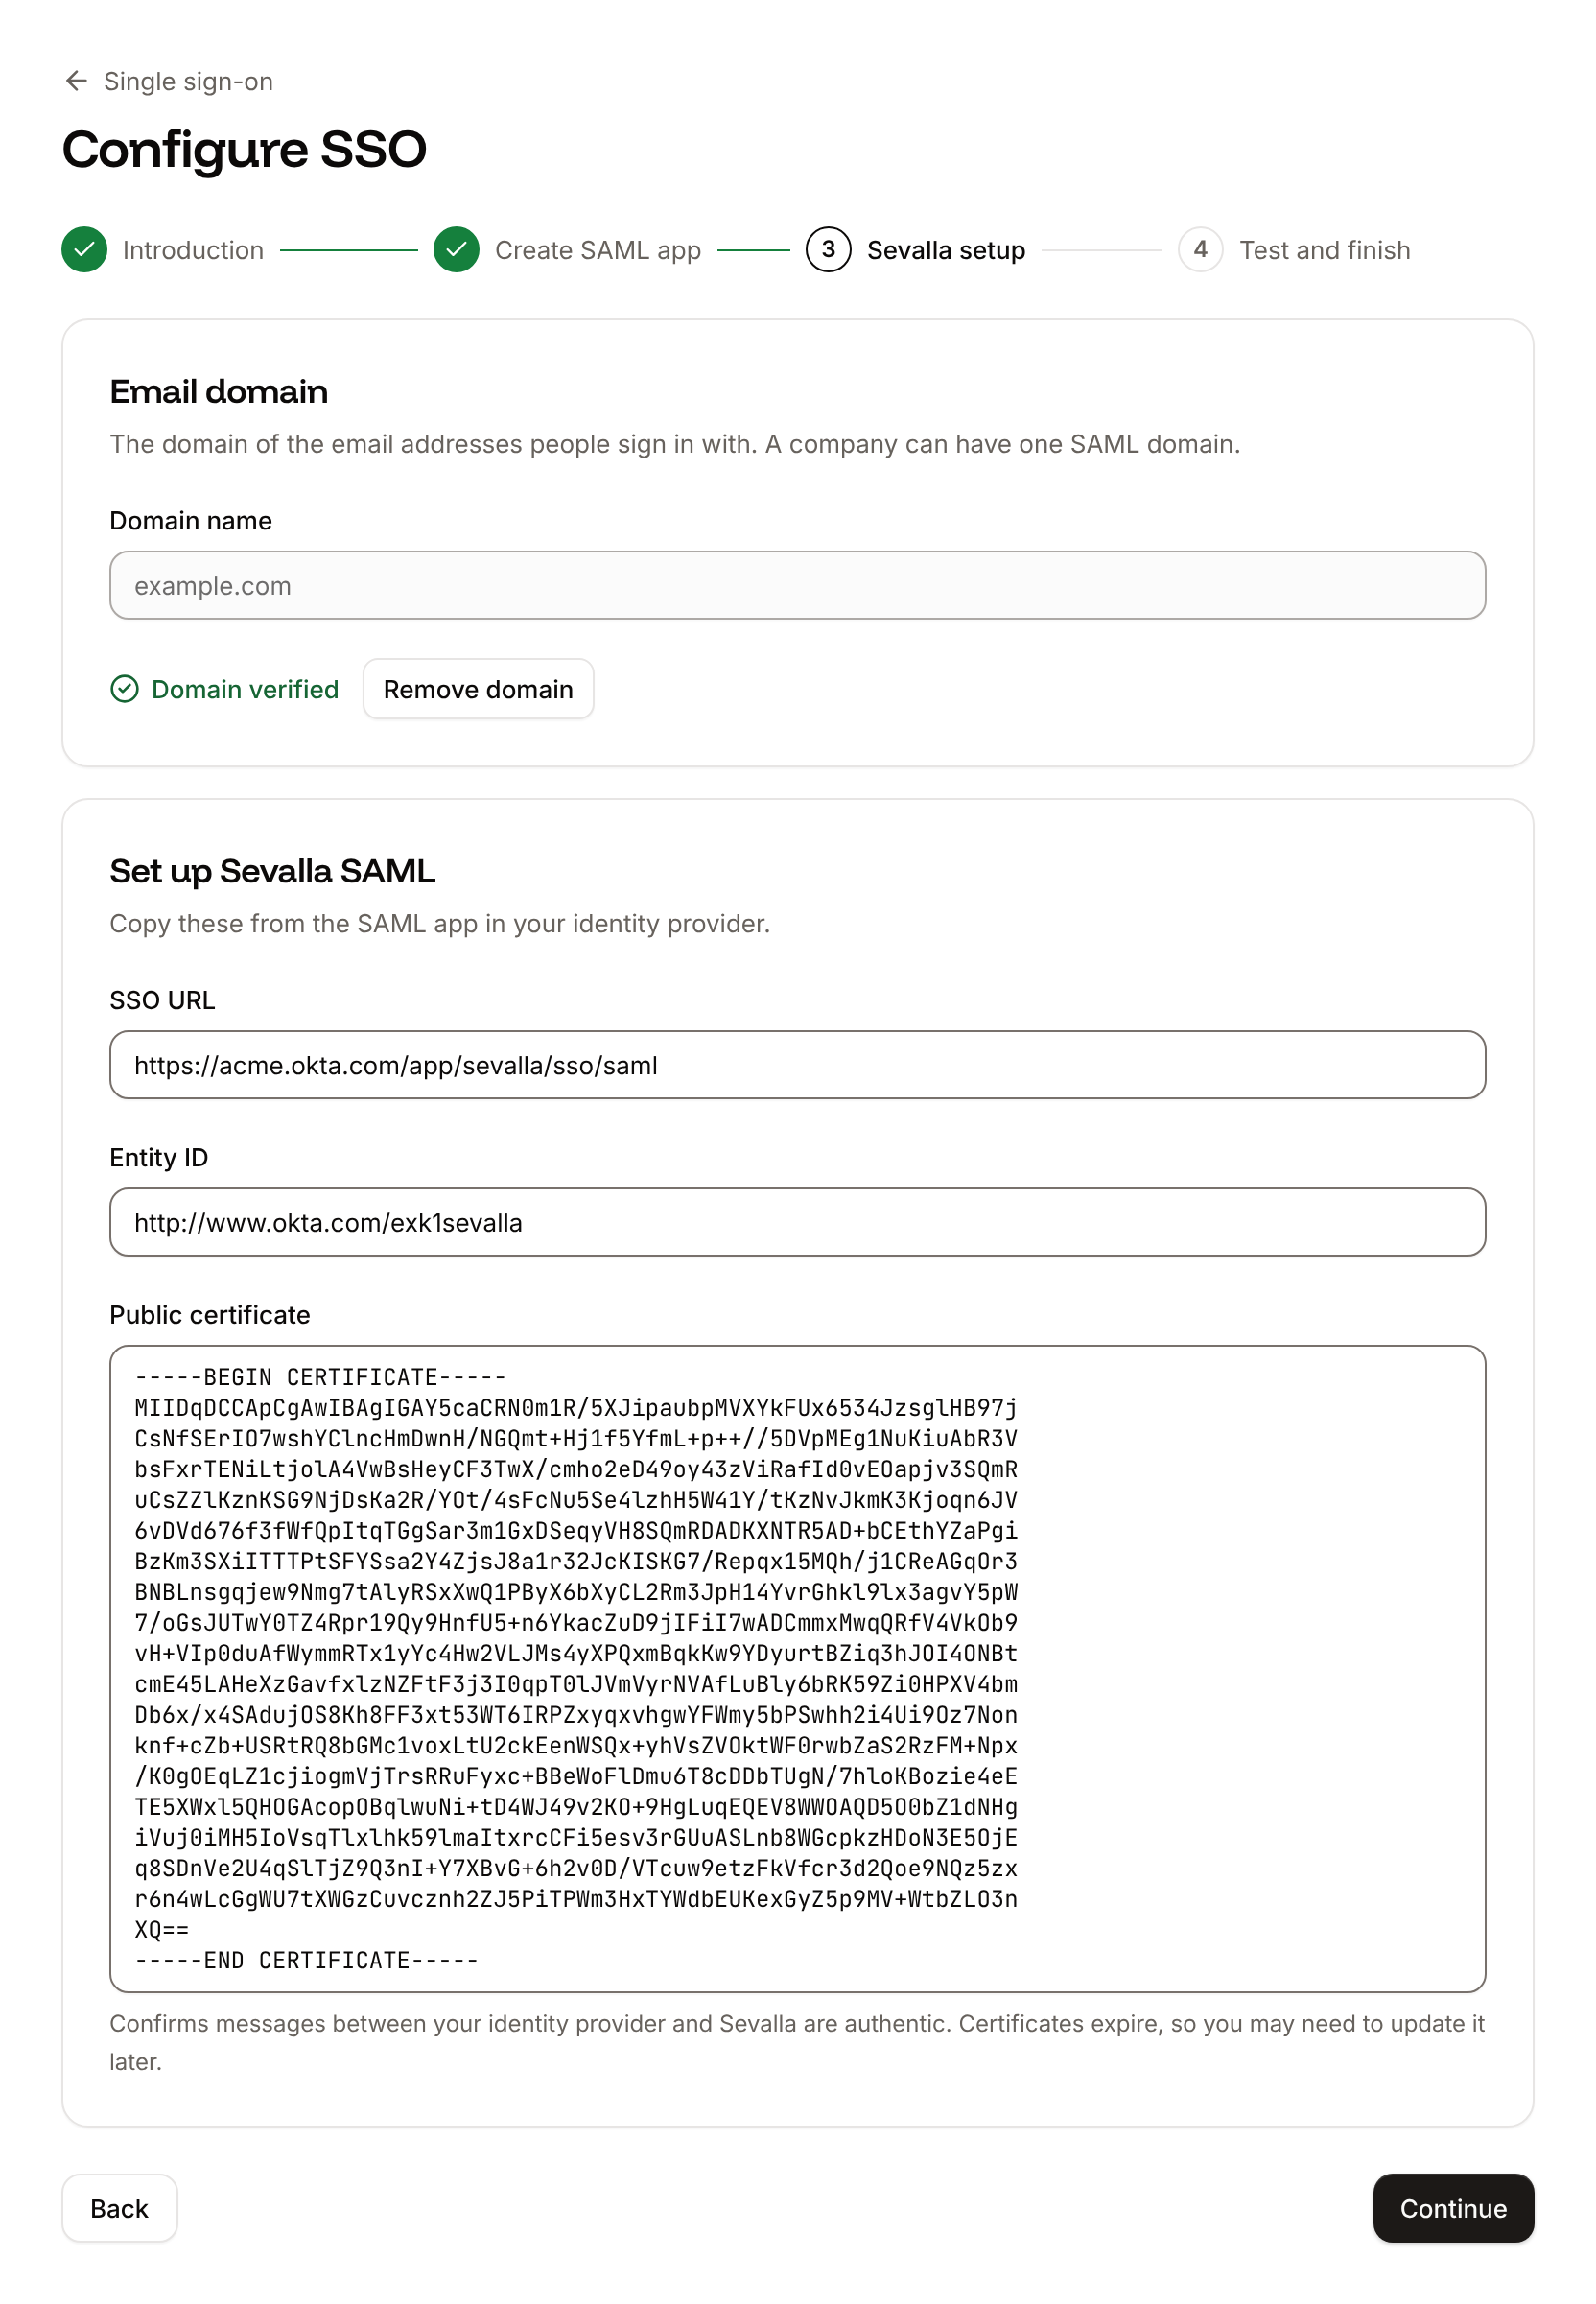
The Sevalla setup step starts with Email domain: the domain of the email addresses people sign in with.1
Add the domain
In Domain name, enter your email domain (for example,
example.com), then click Add domain. If Sevalla can already confirm you own it (for example, its DNS is managed by Kinsta), the domain is verified at once and the wizard shows Domain verified.2
Add the TXT record
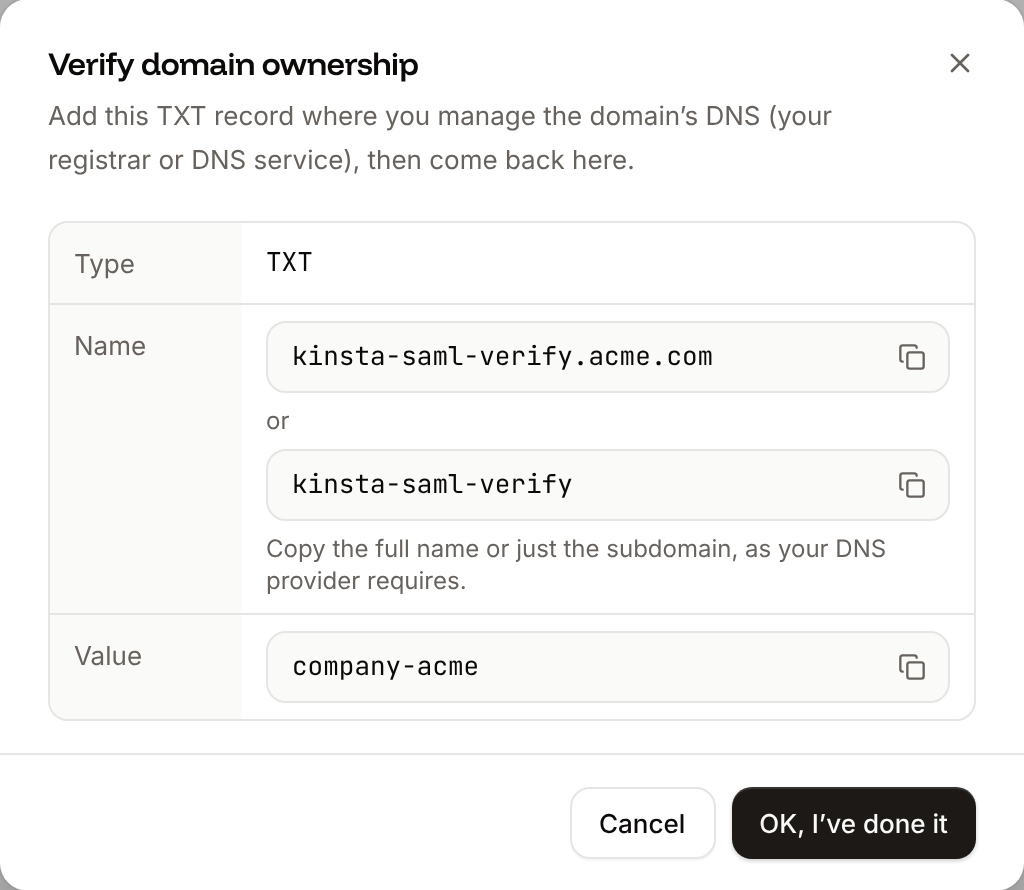
Otherwise, the Verify domain ownership dialog shows a TXT record. Add it where you manage the domain’s DNS:
3
Confirm the record
Click OK, I’ve done it. When Sevalla finds the record, the wizard shows Domain verified.
We could not verify this domain. DNS changes can take up to 24 hours to show. Wait, then click Verify domain to check again. You can also close the dialog and come back to the wizard later. If another company already verified the domain, Sevalla shows This domain cannot be used.
To use a different domain, click Remove domain and add the new one.
Add the identity provider details
Under Set up Sevalla SAML on the same step, paste the values from the SAML app you created in your IdP:
Continue turns on once the domain is verified and all three fields are filled. Click it to go to Test and finish.
Test and set SSO live
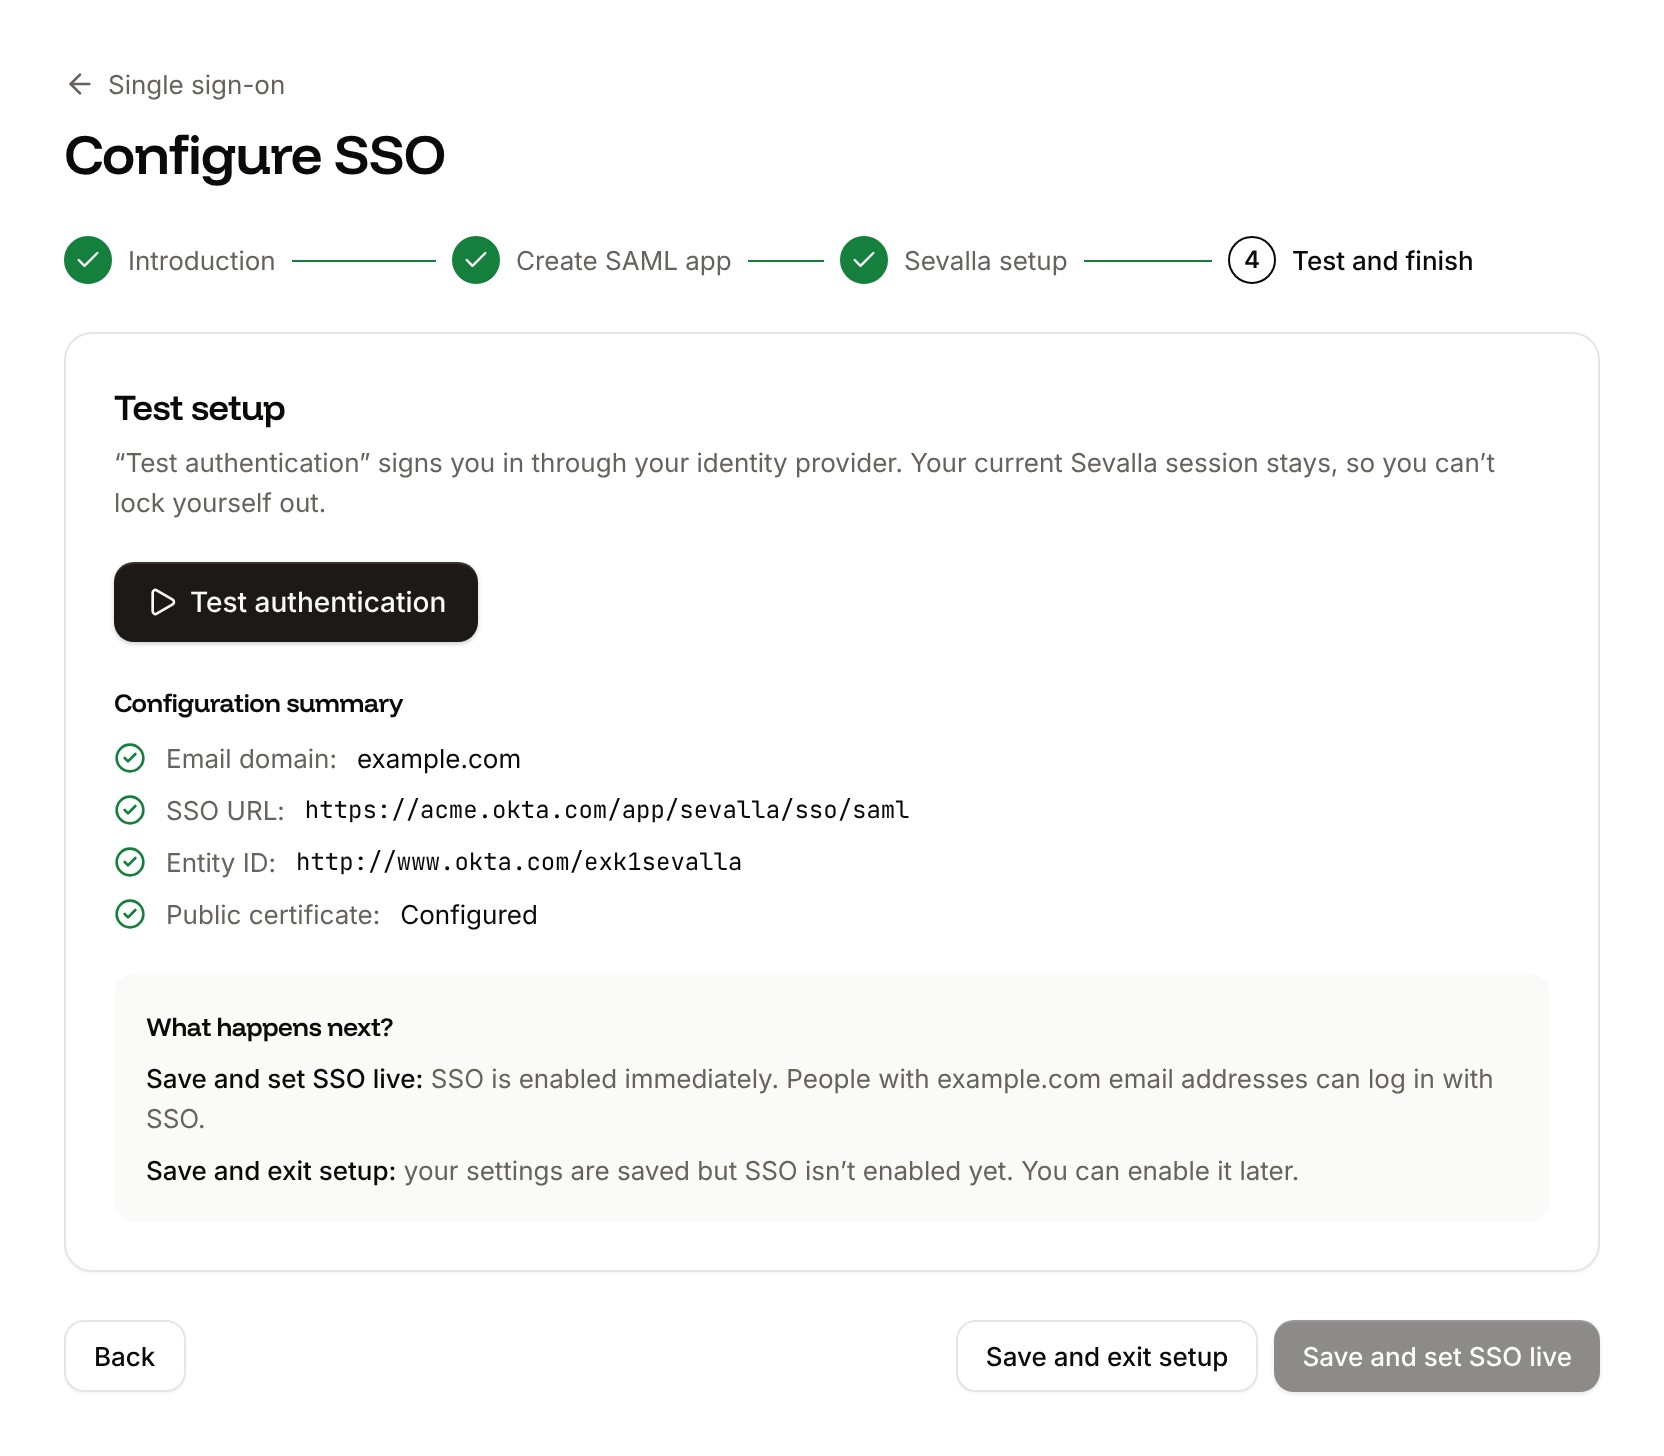
Sevalla only sets SSO live after a successful test. The test signs you in through your IdP; your current Sevalla session stays, so you can’t lock yourself out.1
Run the test
On Test and finish, check the Configuration summary, then click Test authentication. Sign in to your IdP when it asks.
2
Check the result
Sevalla brings you back to the wizard.
Authentication test was successful. means it worked. Authentication test failed. comes with the reason; see Troubleshoot SSO sign-in, fix the setting, and test again.3
Set SSO live
Click Save and set SSO live. To finish later instead, click Save and exit setup: your settings are saved, and SSO stays off until you set it live.
Update the SSO configuration
To renew the IdP certificate or change any other value, click Change on the Single sign-on card. The wizard opens with the current values. Make your changes, run Test authentication, then click Save and set changes live. Until you do, the live configuration keeps working.Make SSO mandatory
Mandatory single sign-on requires everyone in the company to authenticate through your IdP, except the people on the exceptions list.1
Turn it on
On the Mandatory single sign-on card, click Enable.
2
Review who's affected
If SSO is already live and some people in the company don’t use an email address on your SSO domain and aren’t exceptions, the dialog shows People will get locked out with how many. Change their email address to one on the domain, add them as exceptions, or remove them from the company.
3
Keep a way back in
Leave the option to add the company owner to exceptions selected (it’s labeled with the owner’s name and selected by default), so the owner can still sign in with a password if your IdP has a problem.
4
Confirm
Click Enable mandatory SSO. The card shows Enabled: SSO only.
Add or remove exceptions
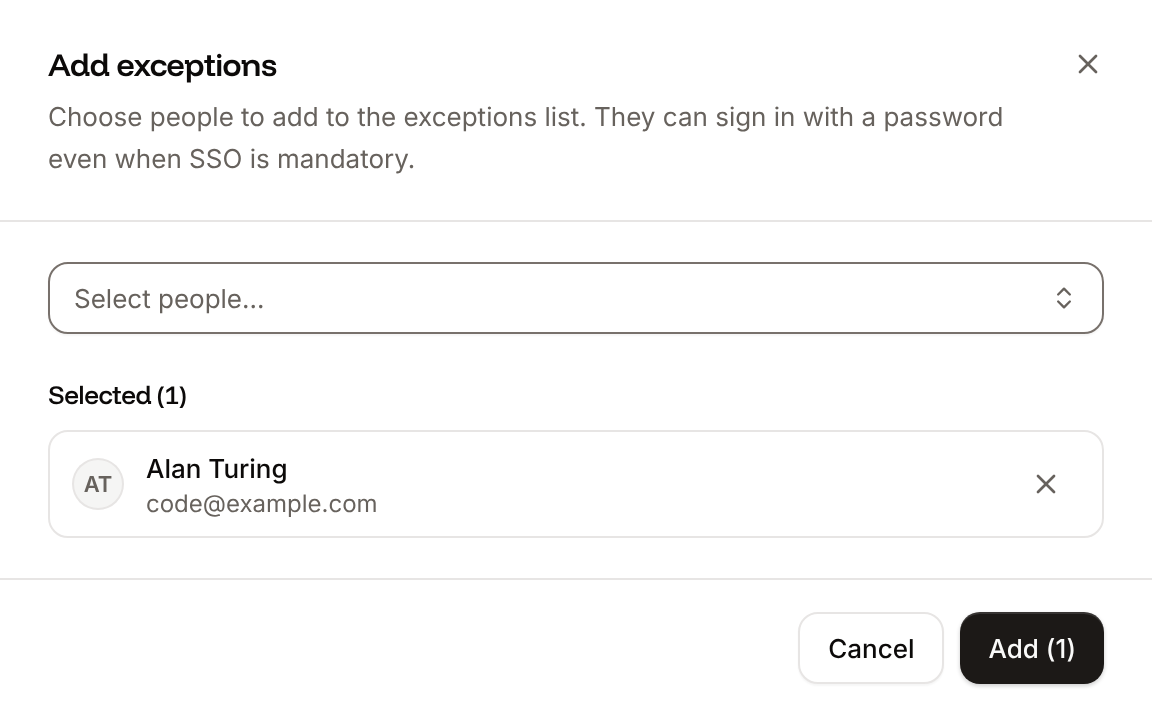
Exceptions are people who can sign in with their password even when SSO is mandatory, for example contractors without an email address on your domain.- Add exceptions: on the Exceptions card, click Add exception. In Select people…, pick one or more people from the company, then click Add.
- Remove an exception: click the trash icon next to the person, then click Remove exception. From then on, they can only access the company through your IdP.
Turn on just-in-time provisioning
Just-in-time (JIT) provisioning lets anyone your IdP allows join the company the first time they sign in with SSO, without an invitation. Their email address must be on your SSO domain. They join with the default role.1
Choose the default role
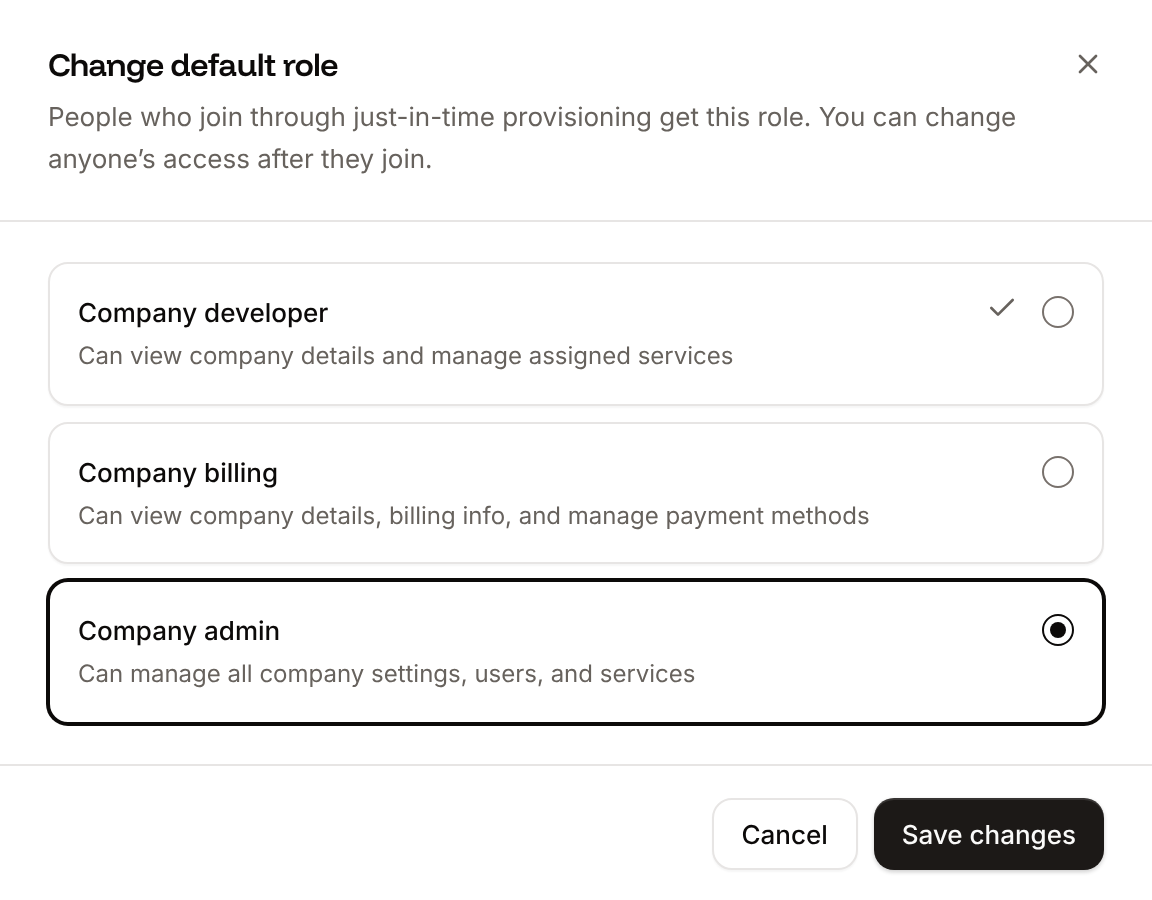
On the Just-in-time provisioning card, click Change default role. Pick Company developer (the default), Company billing or Company admin, then click Save changes. See Users and roles for what each role can do.
2
Turn on JIT
On the same card, click Enable, then click Enable JIT. The card shows Enabled and the default role.
- New people click Sign in with SSO and enter their work email. Sevalla asks them to agree to the Terms of Service and Privacy Policy, then sends them to the IdP. Sevalla creates their account with the name the IdP sends.
- People who already have a Sevalla account with an email address on the domain join the company with the default role when they sign in with SSO.
Remove access
To take someone’s access away completely, remove them in both places:- In Sevalla: remove them from the company. If JIT is on and your IdP still allows them, they can sign in with SSO and join again.
- In your IdP: unassign them from the Sevalla app. If SSO isn’t mandatory, or they’re an exception, they can still sign in with their Sevalla password.
Disable SSO
1
Open the dialog
On the Single sign-on card, click Disable.
2
Help people without a password
If some people have never set a Sevalla password (for example, they joined through JIT), the dialog says how many. Select Send password reset email to users without a password to email them a link to create one.
3
Confirm
Click Disable SSO.
Troubleshoot SSO sign-in
FAQ
How is SAML SSO different from signing in with GitHub, GitLab or Bitbucket?
How is SAML SSO different from signing in with GitHub, GitLab or Bitbucket?
Signing in with a Git provider uses your personal Git account, which you connect yourself on the My account page. SAML SSO uses your company’s identity provider: the company decides who can sign in, can make SSO mandatory, and can add people automatically with JIT.
Why can I still sign in with my password when SSO is mandatory?
Why can I still sign in with my password when SSO is mandatory?
Mandatory SSO applies to one company, not to your Sevalla account. Your password still signs you in to your account and to your other companies. The company with mandatory SSO asks you to authenticate through its IdP before it opens, unless you’re on its exceptions list.
Can a company use more than one email domain for SSO?
Can a company use more than one email domain for SSO?
No. Each company has one SSO domain. People with addresses on other domains can be added as exceptions and sign in with a password.