Before you begin
- You’re a company owner or admin in Sevalla.
- You can add applications in a PingOne environment.
- Your Sevalla account uses an email address on your company’s domain, and you have a PingOne user with the same address. The setup test signs you in with it.
Values to copy
From Sevalla’s Create SAML app step into PingOne:
From the application’s Connection Details in PingOne into Sevalla’s Sevalla setup step:
Start the setup in Sevalla
1
Open the wizard
In the sidebar, under Company, click Single sign-on. On the Single sign-on card, click Enable (or Continue setup).
2
Go to the values
Click Continue to reach Create SAML app. Keep this tab open: you’ll copy its values into PingOne.
Create the SAML app in PingOne
1
Start a new application
In the PingOne admin console, open the environment your users are in, go to Applications > Applications, and click the + button to add an application.
2
Name the application
In Application Name, enter
Sevalla. Optionally add the description and upload the Sevalla logo as the Icon. Select SAML Application, then click Configure.3
Enter the SAML configuration
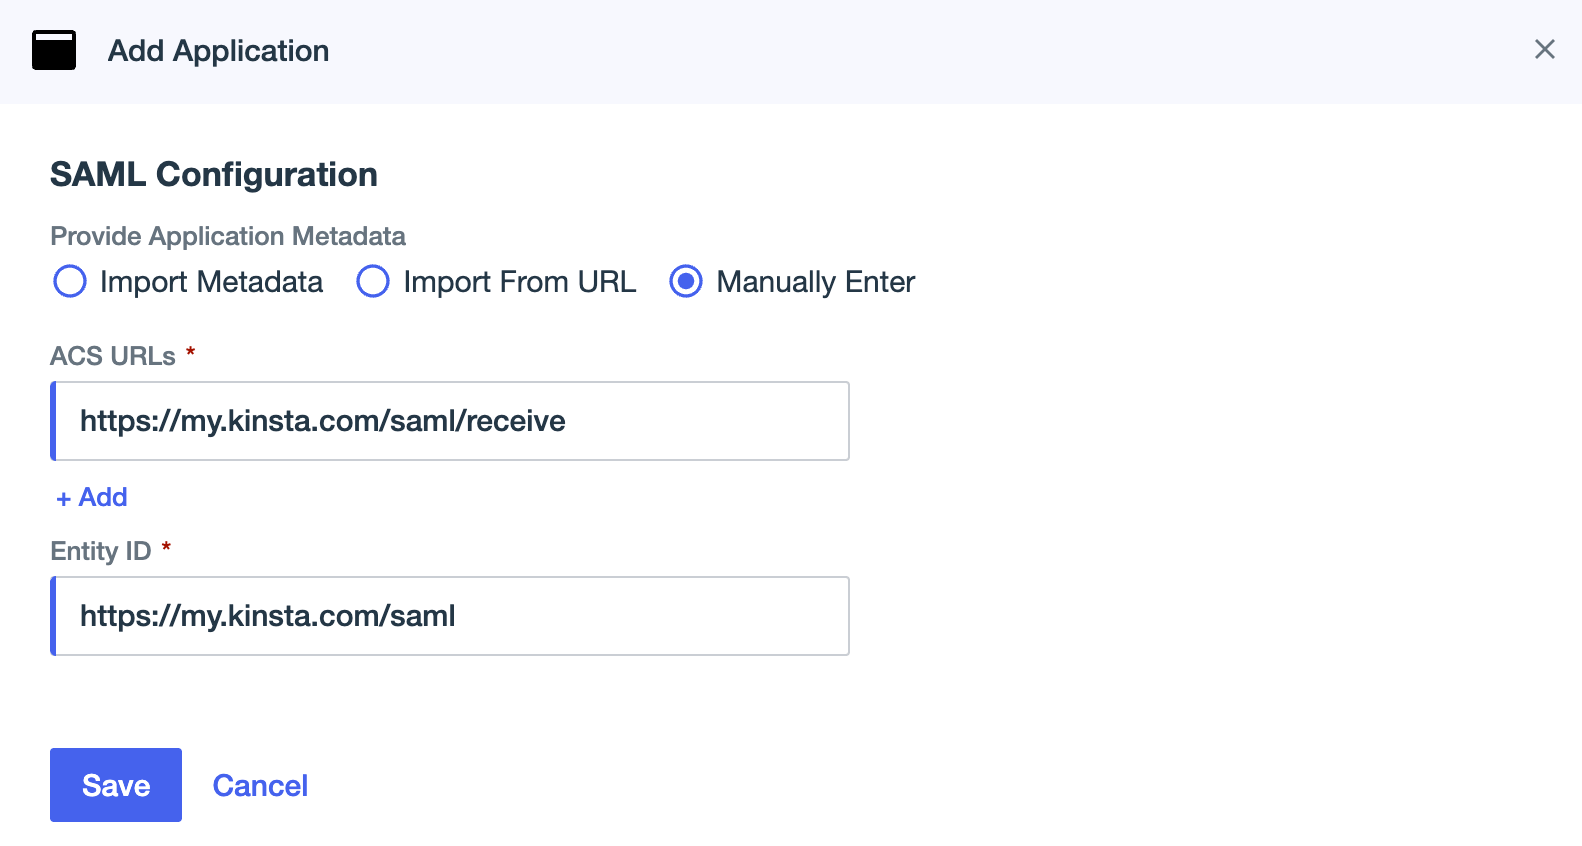
Select Manually Enter. In ACS URLs, enter
https://my.kinsta.com/saml/receive. In Entity ID, enter https://my.kinsta.com/saml. Click Save.4
Map the attributes
Click the Attribute Mappings tab, then click the edit (pencil) icon. Map
saml_subject to Email Address, so the Name ID is the person’s email. Click Add for each of these rows and select Required on each:Click Save.
5
Turn the application on
Turn on the toggle at the top of the application’s details. A new application stays off until you do.
Give people access to the app
To limit the application to some people, click its Access tab, click the edit (pencil) icon, and pick the groups that may use it. Include yourself, so you can run the test.Add the PingOne details to Sevalla
1
Open the connection details
In PingOne, click the Sevalla application, open its Overview tab and scroll to Connection Details.
2
Download the certificate
Click Download Signing Certificate, then select X509 PEM (.crt). Open the file in a text editor.
3
Verify your email domain in Sevalla
In the Sevalla tab, click Continue to reach Sevalla setup. Under Email domain, add and verify your domain. See Verify your email domain.
4
Paste PingOne's values
Under Set up Sevalla SAML, paste:
- SSO URL: PingOne’s Initiate Single Sign-On URL
- Entity ID: PingOne’s Issuer ID
- Public certificate: the whole contents of the certificate file, including the
BEGIN CERTIFICATEandEND CERTIFICATElines
Test and set SSO live
On Test and finish, click Test authentication and sign in to PingOne. When Sevalla showsAuthentication test was successful., click Save and set SSO live. If the test fails, see Troubleshoot SSO sign-in.
Next, you can make SSO mandatory and turn on just-in-time provisioning.